Shortlisting a supplier for a national ID or e-passport program is not a procurement exercise you can win on price. The credentials you are sourcing will carry a citizen’s legal identity, biometric references, and often the keys to border control for a decade or more. A single weak link—an uninspected clean room, an uncleared operator, a reused chip batch—can become a national-security incident. This guide gives government and institutional buyers a practical factory-audit checklist: what to verify, what to demand in writing, and the red flags that should stop a shortlist in its tracks.
Why a Factory Audit Is Non-Negotiable for National ID and e-Passport Programs
The documents at the center of these programs are among the highest-value targets in any economy. A national ID card or e-passport is, by design, accepted as proof of identity at borders, banks, and government counters. If a supplier cannot prove how those documents are made, personalized, and protected, you are not buying a product—you are inheriting a vulnerability. For programs that must stay trustworthy for five to ten years, the cost of a weak supplier is measured in recalls, data breaches, and lost public confidence, not in the per-card line item.
Most of the value sits inside the card itself. Modern credentials embed fused polycarbonate layers, laser-personalized security printing, and a contact or contactless chip holding biometric and cryptographic data. Choosing the right base material and construction is a procurement decision in its own right—see our breakdown of polycarbonate vs PVC vs PETG for government ID. What an audit adds is assurance that the supplier actually controls those layers end to end.
The international baseline is clear: ICAO Doc 9303 defines the global specification for machine-readable and biometric travel documents. A credible supplier should be able to demonstrate, with evidence, that its cards and personalization processes are designed to that standard—not merely claim compliance in a cover letter.
Security Certifications and Plant Accreditations to Verify
Certificates are the first filter, but only if they are real, in-scope, and current. For secure printing, the dedicated reference is ISO 14298 (management of security printing processes). It sits on top of the universal ISO 9001 quality-management baseline, which on its own is necessary but not sufficient for a high-security program.
- ISO 14298 – security-printing process management; confirm the scope covers your product type and is currently valid.
- ISO 9001 – baseline quality management; expect it, but do not treat it as proof of security.
- Common Criteria (ISO/IEC 15408) – relevant when a smart-chip operating system or applet is part of the deliverable; verify the certificate on the Common Criteria Portal.
- EMVCo approval – mandatory for any payment-capable credential; check the product is on the EMVCo approval list.
- National accreditations – personalization-bureau licensing or site clearance required by your own tender law.
Do not accept a screenshot. Demand the original certificate, confirm it is in scope for the product you are buying, and cross-check the issuing body. Our guide to smart card certifications decoded explains what each scheme actually covers and where suppliers commonly overstate their claims.
Physical and Information Security of the Production Site
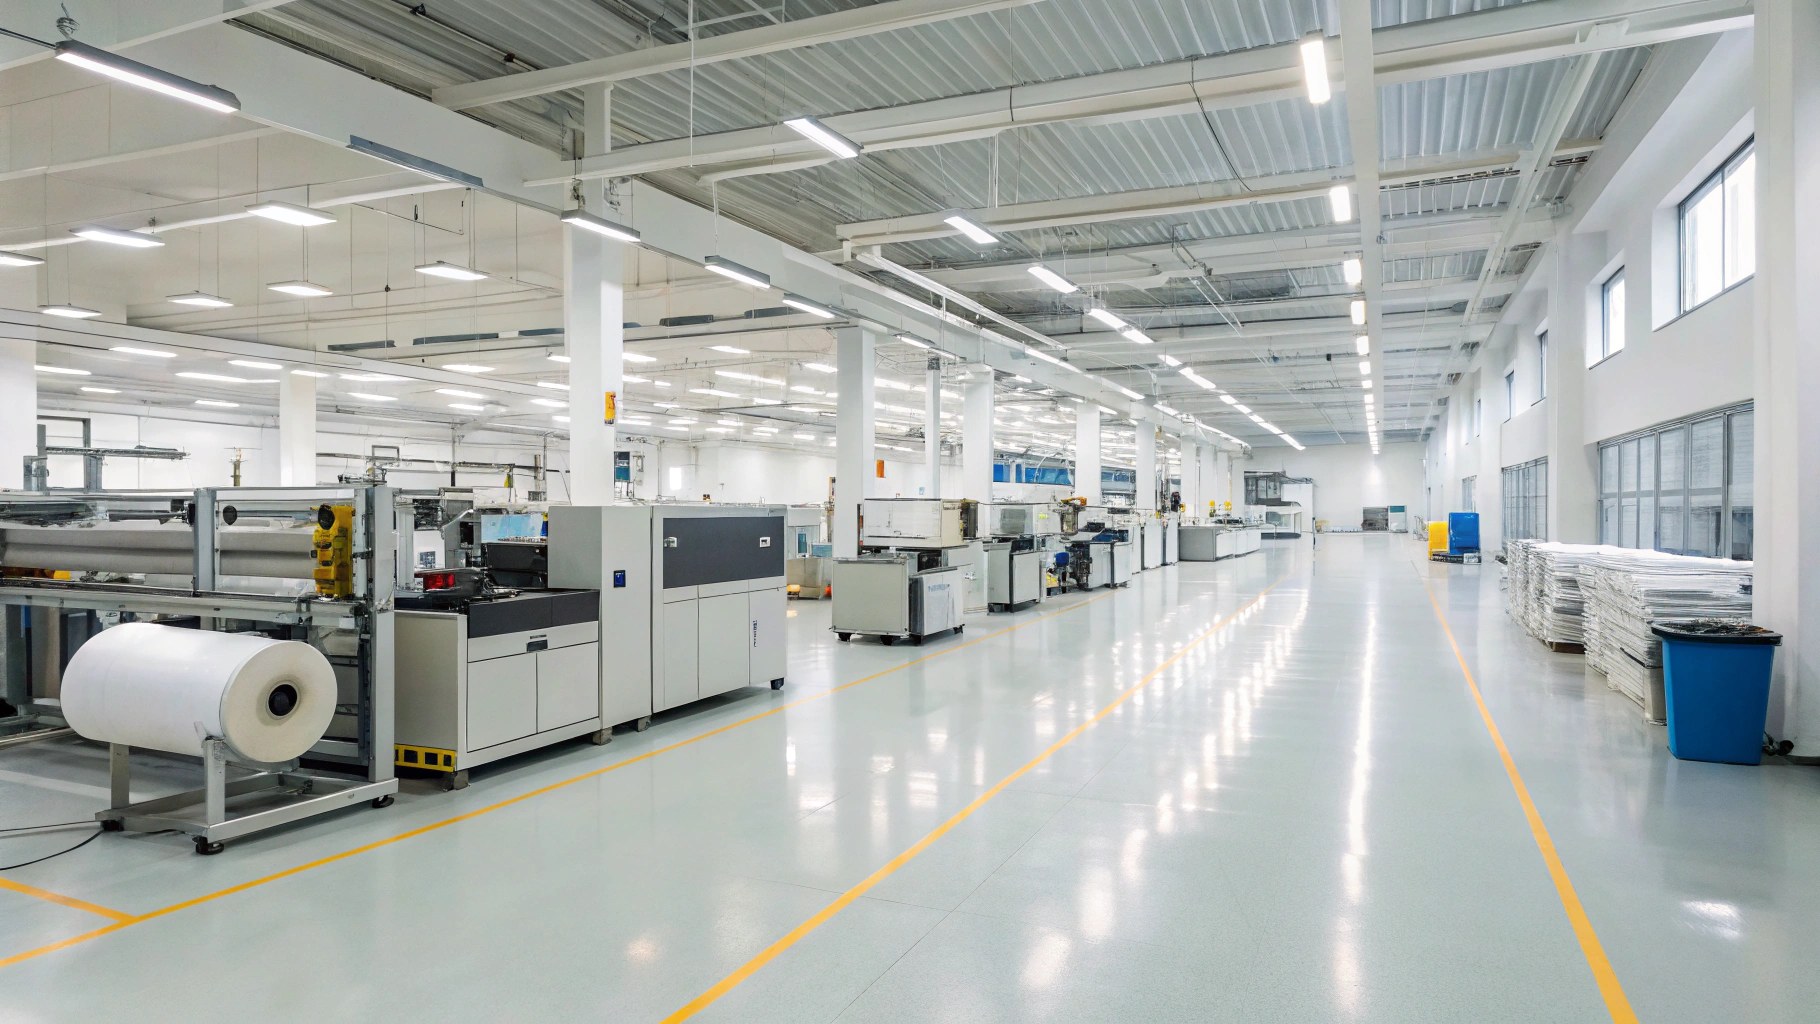
A genuine high-security plant segregates blank cards, chips, and personalization data into physically separate, independently logged zones. Expect 24/7 CCTV with defined retention, visitor logging, and vetted, background-checked personnel in secure areas. Networks used for personalization should be segregated or air-gapped from the general office, with no uncontrolled data egress.
If a supplier’s tour blends the personalization room, the chip store, and the data server into one open floor, treat it as a warning sign, not a convenience. The physical layout is the simplest, most honest signal of how seriously a plant takes insider risk.
Personalization, Key Management, and Data Protection
Personalization is where identity data meets the physical card, and it is where most programs fail quietly. Ask precisely how cardholder data is received, encrypted, stored, and destroyed. Encryption must apply in transit and at rest, with a documented data-flow diagram you can hand to your security team.
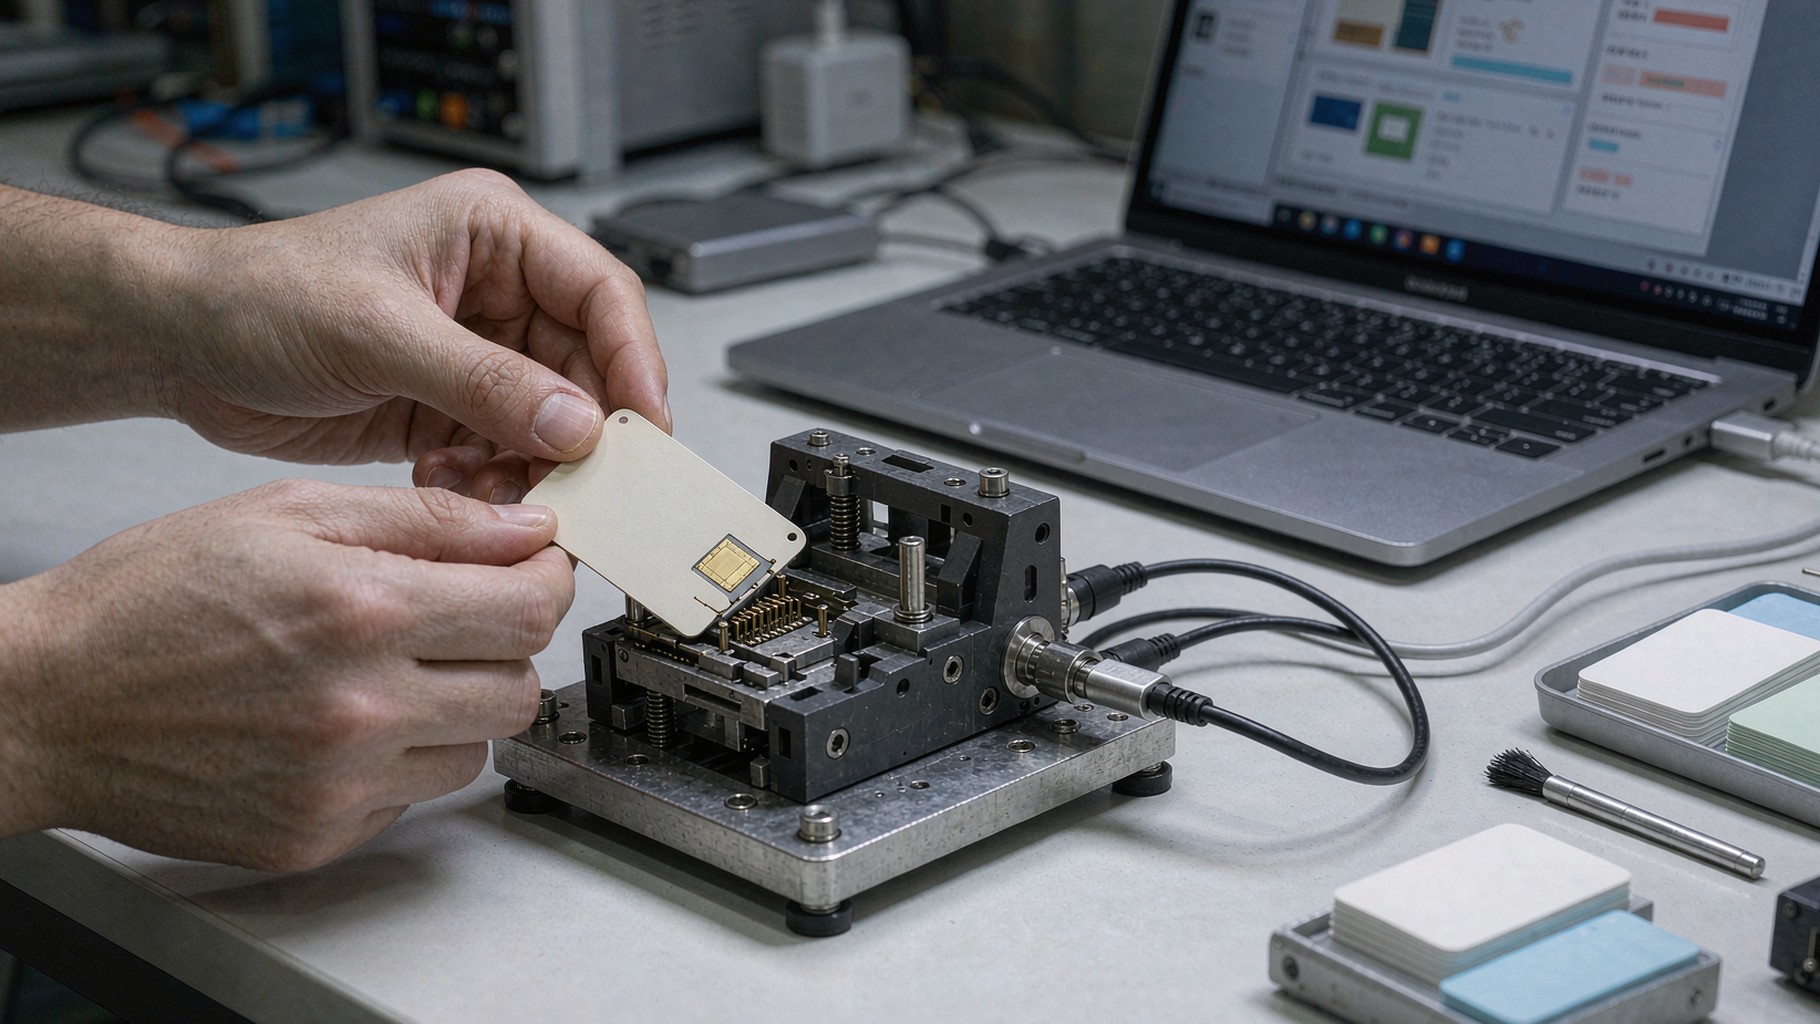
Key custody is the crux. Cryptographic keys should be loaded via an HSM or SAM inside a secure room, under dual-control and split-knowledge procedures. No key should ever exist in clear text on a general-purpose workstation, and no key should be exportable once loaded. After each batch, require a data-deletion certificate, not just assurances. For the printing side of personalization, our comparison of dye-sublimation, re-transfer, and laser engraving covers which method suits which security level.
Quality Assurance, Material Traceability, and Lifetime Testing
Audit the quality system, not the sales deck. Incoming material inspection should trace every chip, inlay, and module batch to its source, and lot-level genealogy should follow each card through production. In-process and end-of-line testing should reference ISO/IEC 10373-1 for mechanical, thermal, chemical, and electrical performance.
A credible supplier shows you the test reports with batch numbers, not a generic brochure—and can reproduce a sample to the same specification six months later. For acceptance at goods-in, adapt the practical checks in our card shipment inspection checklist. Insist on durability and lifetime-testing evidence that matches your program’s five-to-ten-year horizon.
Supply-Chain Provenance and Component Sourcing
You are not only auditing the prime contractor; you are auditing everyone who feeds it. Ask where chips, modules, inlays, inks, and overlays originate, and require dual-sourcing where single-source risk exists. Undocumented component provenance can introduce counterfeits or export-controlled parts that nullify your tender’s compliance clauses, so demand documented due diligence on conflict minerals and export controls—and reserve the right to audit sub-suppliers, not just the prime.
Track Record, References, and Audit-Day Red Flags
Finally, weigh the supplier’s operating history. Existing government programs, anonymized references, and past site-audit reports are strong signals; so is demonstrable capacity to scale to national volumes without subcontracting the secure steps. Watch for red flags during the visit: reluctance to show the personalization room, vague answers on key custody, missing original certificates, high turnover in security roles, or no documented incident-response plan. Building anti-counterfeit resilience into the card is only half the story—our piece on making ID cards harder to forge shows what that resilience should look like on the card itself.
Frequently Asked Questions
How long does a proper factory audit take?
For a national program, a credible on-site audit typically spans two to five days—covering certification review, a physical-security walkthrough, personalization and key-management interviews, and QA-record inspection. Rushed half-day visits rarely surface the issues that matter.
Is ISO 14298 enough on its own?
No. ISO 14298 governs security-printing process management and should be complemented by ISO 9001, the relevant Common Criteria or EMVCo approvals, and any national accreditation your tender requires. Treat it as one layer of a stack, not the whole case.
Can we audit the supplier remotely?
Remote document review is a useful first pass, but physical verification of secure zones, key-loading procedures, and personnel controls requires an on-site visit before you award the contract. Do not let a polished video tour substitute for walking the floor yourself.
Evaluating a secure printing factory is ultimately about trust you can evidence, not trust you are asked to assume. If you are preparing a national ID or e-passport tender, contact our team for a factory-evaluation pack, accreditation summary, and material samples you can verify against this checklist.